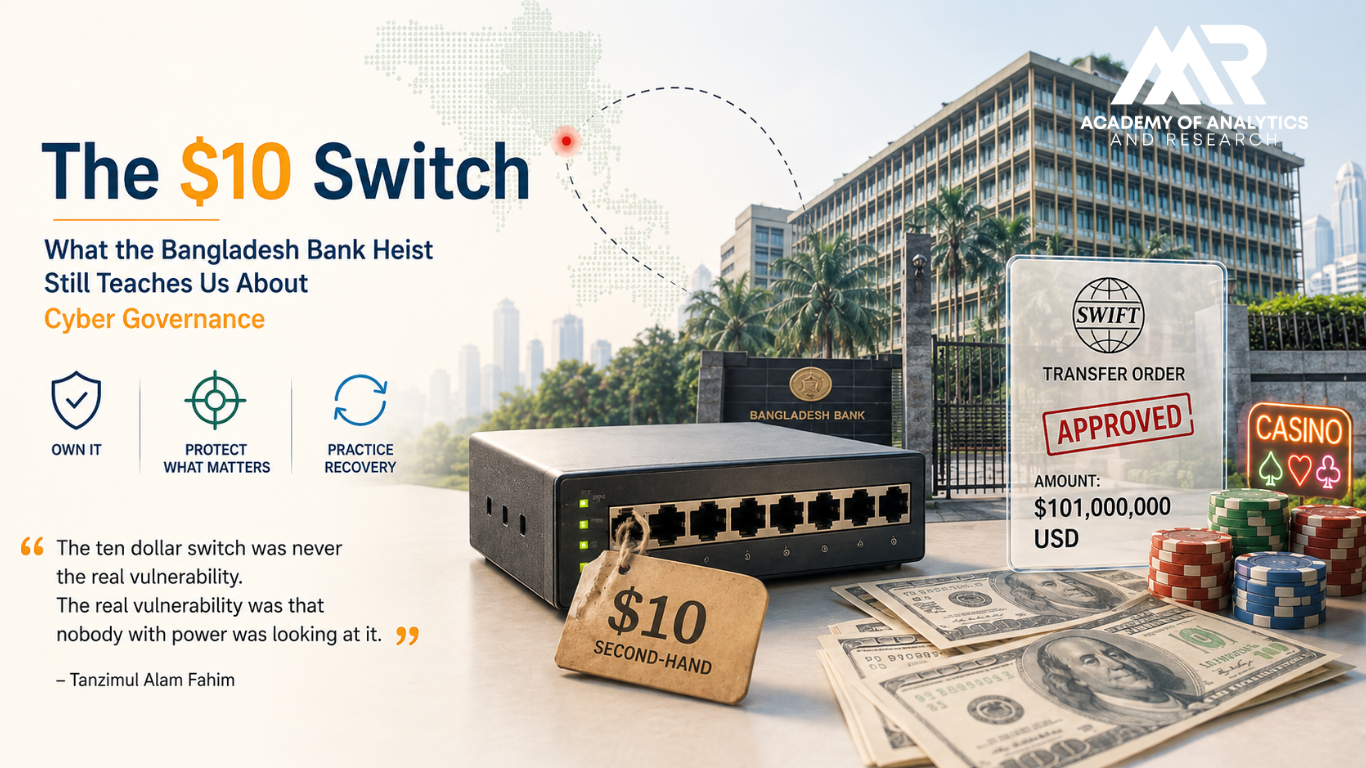
In February 2016, thieves attempted to steal nearly one billion dollars from the central bank of Bangladesh without setting foot in the country. After months of quiet reconnaissance inside Bangladesh Bank’s network, they used the bank’s own credentials to issue thirty-five fraudulent transfer instructions over the SWIFT network, drawing on the bank’s account at the Federal Reserve Bank of New York. Most of the instructions were blocked or reversed. Five went through. About 101 million dollars left the account. Twenty million bound for Sri Lanka was recovered after a routing bank noticed that the recipient, supposedly a foundation, had been misspelled as “fandation.” The remaining 81 million dollars landed at a bank in the Philippines and vanished into the casino industry within days.
Read that again. One of the largest bank robberies in history was partially stopped by a typo.
The investigation that followed produced a detail that has stayed with me ever since. A Bangladeshi police investigator told Reuters that the bank had no firewall on the relevant network and had connected its SWIFT infrastructure using second-hand switches that cost about ten dollars each. The attackers, later identified by the US Federal Bureau of Investigation as operatives working for North Korea, had spent months preparing a sophisticated intrusion. The defense they had to beat was a ten dollar switch.
The comfortable lie about cyber attacks
When an organization gets breached, the instinct is to tell a technology story. The malware was advanced. The attackers were state sponsored. No one could have stopped it. This story is comfortable because it assigns blame to machines and foreign adversaries, and it is usually wrong, or at least badly incomplete.
The Bangladesh Bank network was flat, meaning that once attackers got in anywhere, they could move almost everywhere. The SWIFT terminals were not isolated from the rest of the bank. Monitoring was thin enough that the intruders operated inside the network for months without detection. None of these are technology failures. They are decisions. Someone decided what the security budget would be. Someone decided that network segmentation could wait. Someone decided, or more likely never consciously decided, that no single executive owned cyber risk.
That is what governance means in this context. Not paperwork, but the chain of decisions and accountability that determines whether the technical people ever get the mandate, the money, and the attention to do their jobs.
The pattern repeats across the most damaging incidents of the past decade. The NotPetya malware that spread from Ukraine in June 2017 crippled the shipping giant Maersk, which had to rebuild roughly 45,000 computers and 4,000 servers in about ten days and reported losses in the range of 250 to 300 million dollars. A US government assessment put NotPetya’s global damage at around ten billion dollars. Maersk was not even a target. It was collateral damage in a geopolitical conflict, transmitted through a piece of Ukrainian tax software the company needed to operate in that market. No firewall vendor sells a product for that. What limits that kind of exposure is knowing what software runs in your organization, which suppliers can reach your systems, and how fast you can rebuild. Those are governance questions.
Why this matters most for developing economies
For countries like Bangladesh, and for much of South and Southeast Asia, this argument is not academic. These economies are digitizing at remarkable speed. Mobile financial services move money for tens of millions of people who never held a bank account. Governments are shifting citizen services, land records, and payments online. Every one of these gains is real, and every one of them concentrates risk in systems that did not exist a generation ago.
The uncomfortable truth is that digital adoption in fast-growing economies tends to outrun the governance that should accompany it. Institutions acquire technology faster than they acquire security leadership, risk management practice, and trained people. The gap between the two is precisely where incidents like the 2016 heist live. The attackers did not beat Bangladesh’s technology. They beat the space between the technology and the institution.
Closing that gap does not require inventing anything. The frameworks already exist. ISO 27001 describes how to run a security management system. The NIST Cybersecurity Framework gives boards and regulators a common language for identifying, protecting, detecting, responding, and recovering. Central banks in the region and beyond have published binding guidance on IT risk. The hard part has never been the absence of standards. The hard part is ownership: a named person accountable for cyber risk, reporting to leadership that actually reads the reports, with a budget defended in the same meetings where other institutional risks are discussed.
Three questions instead of a checklist
Leaders who cannot evaluate a firewall configuration can still govern cyber risk, the same way board members who cannot audit a ledger still govern financial risk. It starts with three questions asked persistently.
First, who owns this? If the honest answer is “the IT department,” the organization has a gap, because IT departments implement decisions but rarely have the authority to force them onto business units, vendors, and executives.
Second, what would hurt us most? Not every system deserves equal protection. A central bank’s payment infrastructure, a hospital’s patient records, a think tank’s donor data and unpublished research all have different worst cases. Institutions that have not ranked theirs are defending everything, which in practice means defending nothing well.
Third, when did we last practice failing? The organizations that survive incidents are the ones that have rehearsed them. Maersk recovered in ten days partly because it could still find one uninfected copy of a critical directory server, on a machine in Ghana that happened to be offline during the attack. That is luck. Recovery should not depend on luck.
A decade after the heist, Bangladesh Bank’s stolen 81 million dollars remains mostly unrecovered, tangled in litigation across multiple countries. The money is gone, but the lesson is still available, and it costs nothing to take: the adversaries are organized, funded, and patient, and they are not primarily attacking computers. They are attacking institutions. Institutions are defended in the boardroom first and at the keyboard second. The ten dollar switch was never the real vulnerability. The real vulnerability was that nobody with power was looking at it.
Author : Tanzimul Alam Fahim
Director of Cybersecurity Research, Academy of Analytics and Research – AAR